
Transforming Risk Management in the Payment Industry with ISO 20022 Standards

Updated: Sep 16

ISO 20022 is changing more than the format of payment messages. It is changing the information available to understand, process and manage payment risk.
As ISO 20022 adoption becomes more established across domestic and cross-border payment infrastructures, financial institutions have access to richer and more structured information about the payment instruction, the parties involved and the purpose of the transaction. This creates opportunities to improve financial crime controls, reconciliation, automation, investigations and wider risk analysis.
But richer data does not automatically produce better risk management.
The value depends on whether that information is accurate, preserved as it moves through the payment chain and made available to the systems and controls that can use it. Poor-quality data can be processed more efficiently without producing better decisions. Information can be transformed or lost between systems. Greater interoperability can reduce integration friction without creating operational resilience. Third parties can also become critical dependencies in how payment data is handled.
For risk leaders, the important question is therefore no longer simply whether the organisation has adopted ISO 20022. It is whether the richer information it provides is changing how payment risk is identified, understood and managed in practice.
This article explores that question across the areas where the impact is most significant: risk visibility, financial crime, reconciliation and exceptions, data quality, interoperability, cross-border payments, governance and third-party dependencies. It also considers the indicators risk leaders can use to determine whether the expected benefits are actually being realised.
ISO 20022 provides the capability for better-informed payment risk management. What organisations do with that capability determines the outcome.
What ISO 20022 Changes for Payment Risk Management
ISO 20022 changes the information available around a payment.
Traditional payment messages were designed around relatively constrained data structures. Information could be limited, inconsistently formatted or embedded within free-text fields, making it harder for systems to interpret transaction data consistently and at scale.
ISO 20022 provides a common framework for exchanging structured financial messages. It allows payment messages to carry richer and more granular information about the parties, purpose and context of a transaction in fields that can be interpreted systematically by different systems.
For risk management, the significance is not simply that firms receive more data in real-time. It is that information can be more structured, consistent and machine-readable.
This can improve the ability of payment firms and financial institutions to:
identify and validate parties and transaction information;
apply automated screening and monitoring rules;
distinguish transactions using richer contextual information;
investigate unusual or potentially suspicious activity;
automate reconciliation and exception handling; and
analyse payment activity and emerging risk patterns across larger transaction populations.
The potential result is a shift from risk controls that rely heavily on fragmented transaction information and manual interpretation towards controls capable of using richer payment context at scale.
Richer Data Does Not Automatically Mean Better Risk Management
The distinction is important. ISO 20022 enables better risk management. It does not guarantee it.
A structured field creates little value if it is incomplete, inaccurate or populated inconsistently. Greater machine readability does not improve a control if the underlying screening rules are poorly calibrated. More transaction information does not produce better decisions if relevant data is lost or transformed as a payment moves between systems.
The risk-management benefit depends on what happens to the information after it enters the payment chain.
A firm needs to understand whether:
relevant fields are populated with sufficiently accurate and complete data;
information remains intact as messages move between internal and external systems;
systems and controls can consume and interpret the additional data;
fraud, financial crime and operational controls have been adapted to use it effectively; and
the resulting information improves decisions, investigations and customer outcomes.
This also creates a less obvious risk. Greater automation can amplify poor data or poorly designed rules. If inaccurate information is processed automatically across high transaction volumes, the result may be faster processing without better risk management.
ISO 20022 should be viewed as a data and messaging capability, rather than a risk control in its own right.
Its value comes from the relationship between the standard and the wider control environment:
Structured Data → Better Context → Better Risk Decisions
But that relationship only holds when the data is sufficiently complete and reliable, systems preserve and interpret it correctly, and controls are designed to make effective use of it.
For payment risk management, that is the real change introduced by ISO 20022: the opportunity to move from processing a payment with limited information towards understanding more of the context surrounding that payment.
Want to see how we approach scaling? Read our comprehensive guide on How FinTechs Build a Scalable Risk Management Framework.

Better Payment Data Creates Better Risk Visibility
Risk management depends partly on the ability to understand who is involved in a transaction, what the payment is for, how it relates to other activity and whether anything about it warrants further attention.
ISO 20022 can improve that visibility by allowing more information to be captured in structured fields rather than relying on abbreviated, unstructured or free-text payment data.
Depending on the payment message and scheme requirements, this can include more detailed party information, structured remittance information, purpose data and identifiers such as Legal Entity Identifiers (LEIs).
Individually, these fields provide additional information. Combined, they can create a richer picture of the transaction and the relationships surrounding it.
The significance for risk management is not simply having more data. It is having better transaction context.
A transaction amount viewed in isolation may reveal relatively little. Combined with information about the parties, purpose, underlying obligation, payment flow and other available activity, the same transaction may be easier to assess and investigate.
From Payment Data to Risk Visibility
The relationship between richer data and better risk management can be viewed as a progression:
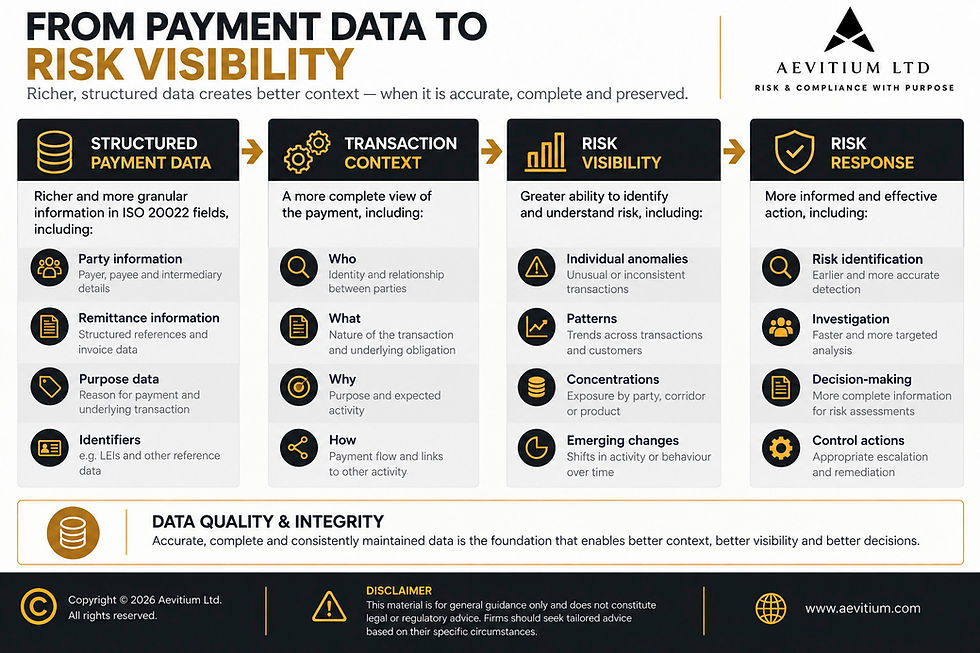
At an individual transaction level, richer context can help firms identify unusual or inconsistent activity and support more targeted investigations.
Across a wider payment population, structured information can also make it easier to identify patterns, concentrations and emerging changes in behaviour. A series of transactions that appear unremarkable individually may become more significant when considered by counterparty, customer, payment corridor, product or over time.
This creates a potentially important shift in risk visibility: from assessing individual transactions largely in isolation towards understanding relationships and patterns across payment activity.
Better Investigations Depend on Preserving the Context
The value of richer information can diminish as a payment moves through multiple systems and organisations.
Fields may be mapped differently between systems, transformed into another message format or truncated, meaning that some information is shortened or lost because a receiving system or message format cannot accommodate it. Internal screening, monitoring or investigation systems may also consume only part of the information contained in the original payment message.
A firm may technically receive ISO 20022 messages without making the full information available to the controls and people that could use it.
This makes data lineage and integrity increasingly important. Firms need to understand where relevant payment information originates, how it moves through the transaction chain, where it is transformed and whether important information remains available for screening, monitoring, reconciliation and investigation.
Data Quality Determines the Value of the Insight
More structured data also creates greater dependence on its quality.
Incomplete party information, inconsistent purpose data or inaccurate identifiers can reduce the effectiveness of automated controls. Poor-quality information can also generate unnecessary exceptions, false positives and additional investigation work.
Greater automation can amplify the problem. If inaccurate or inconsistently interpreted information feeds automated decision-making across high transaction volumes, poor data can result in faster processing without better risk decisions.
The relationship is therefore not simply:
More Data → Less Risk
ISO 20022 creates the opportunity for:
Structured Data → Better Context → Better Risk Visibility → Better Risk Response
But data quality and integrity underpin the entire chain.
For payment firms, this is where the risk-management value of ISO 20022 begins to emerge. The standard can make payment information more usable as risk information, but the benefit depends on whether that information remains accurate, complete, preserved and accessible to the controls and decision-makers that need it.
Financial Crime: Moving from Transaction Screening to Transaction Context
Financial crime controls have traditionally relied on a combination of customer information, transaction attributes, screening data and behavioural indicators. ISO 20022 does not change that fundamental model, nor does it detect fraud, money laundering or sanctions breaches itself.
What it can change is the context available to those controls.
More structured information about parties, payment purpose, remittance details and identifiers can give screening and monitoring systems additional signals with which to assess a transaction. Instead of relying as heavily on isolated fields or free-text information, firms may be able to evaluate more of the relationship between who is paying, who is receiving, why the payment is being made and whether that activity is consistent with what is already known.
Context Can Improve Control Precision
This matters because financial crime controls involve more than identifying suspicious activity. They also need to distinguish potentially higher-risk transactions from legitimate activity without creating unnecessary disruption.
Sanctions screening illustrates the point. Limited or poorly structured party information can contribute to potential matches that require investigation.
Better structured identifying information may help controls distinguish parties more accurately, although the outcome still depends on data quality, screening logic and the information available from relevant sanctions sources.
The same principle applies to fraud and transaction monitoring. Additional payment context can potentially help firms:
distinguish unusual activity from legitimate transactions more effectively;
combine transaction information with customer and behavioural data;
identify relationships or patterns across multiple payments;
prioritise alerts and investigations using more relevant information; and
refine analytical models as richer data becomes consistently available.
The opportunity is therefore not simply more screening. It is potentially more precise screening and monitoring.
False Positives Are Also a Risk Signal
Richer data should not be judged solely by whether controls generate more alerts.
A poorly calibrated control can turn additional information into additional noise. High false-positive rates increase investigation volumes, consume operational capacity and can delay or prevent legitimate payments. Conversely, overly permissive rules can improve processing rates while weakening financial crime detection.
Firms therefore need to assess whether enriched payment data is improving the quality of control decisions, not merely increasing the amount of information processed.
Useful evidence may include changes in alert quality, false-positive rates, investigation outcomes, processing delays and the ability to identify previously difficult relationships or behaviours.
This creates a more meaningful test of ISO 20022's financial-crime value:
Does richer transaction context help us distinguish risk more accurately?
The answer depends on how effectively the firm combines ISO 20022 data with its customer information, threat intelligence, behavioural analytics and existing financial crime controls.
Reconciliation, Exceptions and Operational Risk
Some of the most immediate benefits of structured payment data may be less visible than fraud detection.
Consistent, machine-readable information can reduce ambiguity as transactions move between systems, making it easier to automate processing, match payments and investigate exceptions. This can support higher levels of straight-through processing (STP) and reduce the manual intervention required to complete or reconcile transactions.
The risk-management significance lies in what happens when that automation works, and when it does not.
Reconciliation Becomes a Test of Data Integrity
Reconciliation is not simply a downstream accounting activity. A break can reveal that information has been lost, altered, interpreted differently or processed incorrectly somewhere earlier in the payment chain.
Structured identifiers, references and remittance information can improve the ability to match records across systems. But ISO 20022 does not eliminate reconciliation risk. Different systems may still transform fields, apply different validation rules or fail to retain information required downstream.
Reconciliation exceptions can therefore provide useful evidence about whether structured payment information is being preserved consistently across the transaction chain.
Fewer Manual Interventions, Greater Dependence on Automation
Greater straight-through processing can reduce human error and operational effort. It also changes the nature of the risk.
As more transactions are processed automatically, firms become increasingly dependent on the quality of:
underlying data;
validation and transformation rules;
system configuration; and
exception logic.
A defect that once affected a small number of manually processed transactions may operate across a much larger population before it is identified.
The objective should therefore not simply be to maximise STP. It is to achieve reliable automation with effective exception detection.
Exceptions Can Reveal Where the Benefits Are Breaking Down
Exception volumes provide a useful counterpoint to measures of processing efficiency.
Repeated payment repairs, message rejections, reconciliation breaks or manual interventions may indicate that the expected benefits of structured messaging are not being realised consistently. The pattern can also help identify where problems sit: with data received from counterparties, internal mappings, legacy systems, third-party processing or downstream interpretation.
Rather than treating exceptions solely as transactions to be cleared, firms can use them as evidence about the quality of the payment process and its underlying data.
That creates a natural connection between ISO 20022 and operational risk management. The standard may support greater automation and more consistent processing, but the risk question is whether firms can identify when data, automation or system interactions begin to behave differently from what was intended.
For the deeper treatment of transaction failures, dependencies, resilience and customer consequences, I would then add a restrained internal link at the end:
Data Quality Becomes a Risk Management Issue
ISO 20022 increases the amount and structure of information available within payment messages. That creates opportunity, but it also increases dependence on the quality, consistency and interpretation of that data.
A field being structured does not mean the information within it is correct.
Party information can be incomplete. Purpose codes can be applied inconsistently. Identifiers can be missing or incorrect. Data can be transformed as it passes between systems. Different institutions may also interpret or populate fields differently while remaining technically capable of exchanging ISO 20022 messages.
These weaknesses matter because increasingly automated controls may rely on that information to make decisions.
Poor Data Can Scale Poor Decisions
Automation changes the potential impact of a data-quality problem.
When a human reviews an individual transaction, incomplete or unusual information may prompt further investigation. When thousands of transactions are processed automatically using the same data field or decision rule, a systematic weakness can be repeated at scale.
Poor-quality data can therefore contribute to:
inappropriate screening or monitoring outcomes;
unnecessary payment repairs and exceptions;
reconciliation breaks;
incorrect routing or processing decisions;
false positives and avoidable manual investigations; and
unreliable risk analytics and management information.
The issue is not simply whether data is present. Its quality needs to be sufficient for the purpose for which it is being used. Incomplete, inaccurate or inconsistently populated information can undermine otherwise well-designed automated controls.
This creates an important consequence of ISO 20022 for risk management. As firms make greater use of structured payment information to automate processing and control decisions, data-quality weaknesses can propagate more quickly and affect larger transaction populations.
The risk is therefore not simply poor data. It is the combination of poor data, automated decision-making and scale.
Data Quality Becomes Part of the Control Environment
This changes the role of data governance in payment risk management. If transaction data is used to screen customers and payments, identify unusual activity, reconcile transactions or support automated decisions, the quality of that data directly affects the effectiveness of those controls.
Responsibility also extends beyond the original payment message. Information may pass through internal platforms, legacy systems, payment processors and other external providers before it reaches the system or control that ultimately uses it. A field that is complete when a payment is initiated may be mapped differently, transformed or truncated later in the process.
Firms therefore need to understand which data their controls depend upon, where that data originates, how it changes as it moves between systems and what happens when its quality deteriorates.
This is the more important risk-management consequence of richer payment data. ISO 20022 can support better-informed decisions, but it also makes the reliability of the underlying information increasingly important. As more decisions are automated, data quality is no longer simply a technology or data-management concern. It becomes part of the control environment itself.
Interoperability Does Not Automatically Create Resilience
ISO 20022 is frequently associated with greater interoperability across the payments ecosystem. That benefit is important, but interoperability and operational resilience are not the same thing.
A common messaging standard can make it easier for financial institutions, payment infrastructures and other participants to exchange and interpret payment information consistently. It can reduce some of the complexity created by different message formats and make integration between compatible systems easier.
That can support resilience, but it does not create it.
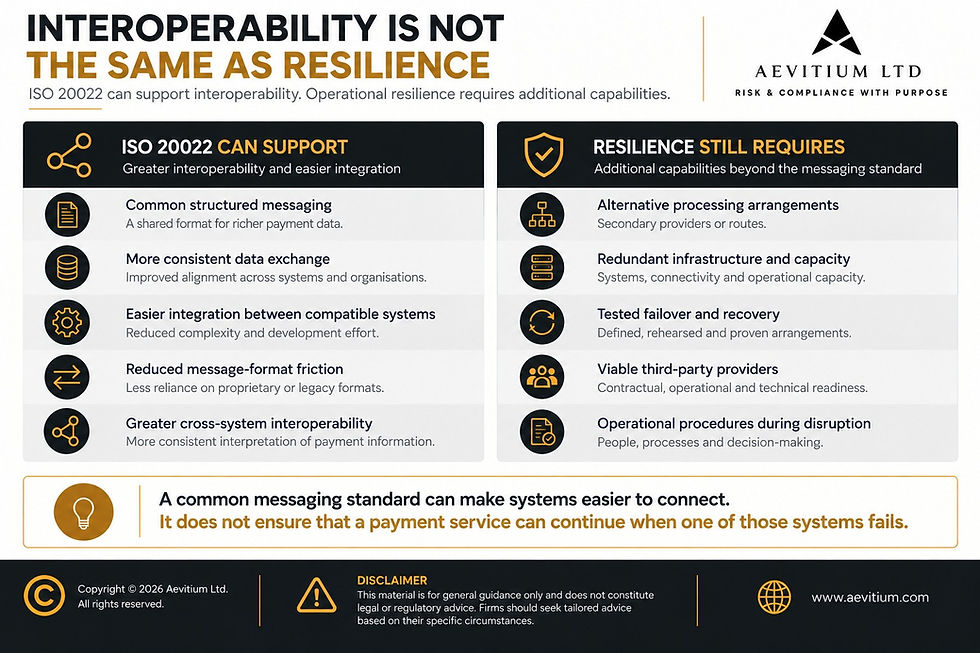
The distinction matters particularly when considering disruption. Two payment systems may both support ISO 20022, but that does not mean transactions can automatically move from one to the other when a service fails.
Continuity depends on whether the firm has actually established the capabilities needed to use an alternative. That may involve technical connectivity, sufficient capacity, contractual arrangements, access to another provider or payment route, compatible operating processes and people who know how to activate and manage the arrangement.
The same applies to recovery. Standardised messaging may reduce some integration barriers, but it does not ensure that dependencies can be restored quickly, that transaction queues can be recovered correctly or that customers can continue to make and receive payments while disruption is occurring.
The Difference Becomes Clear Under Stress
This is where the distinction becomes operationally important.
A firm might have two providers capable of processing the same message format but discover during an incident that switching requires configuration changes, data cannot be transferred as expected, the alternative has insufficient capacity or operational teams have never tested the process.
On paper, the environment appears interoperable. In practice, the payment service may still have a single point of failure.
This corrects an important assumption in the original article, which suggested that ISO 20022 interoperability could allow payments to be rerouted through alternative systems during disruption and thereby create redundancy. Common messaging can make alternative arrangements easier to develop, but those arrangements still need to exist and work.
The resilience value of ISO 20022 should be understood as enabling rather than substitutive. It can reduce some barriers to connecting systems and exchanging information, while the capabilities required to maintain a payment service through disruption still have to be designed, implemented and tested.
ISO 20022 and Cross-Border Payments
The value of consistent payment information becomes particularly important in cross-border payments, where a transaction may pass through several institutions, infrastructures and jurisdictions before reaching its destination.
ISO 20022 provides a common messaging framework that can reduce some of the inconsistency created when payment information is exchanged between participants. But the risk-management benefit depends on more than whether each participant can send or receive an ISO 20022 message.
What matters is whether relevant information remains complete, consistent and usable throughout the payment chain.
A payment may contain detailed party, purpose and remittance information when it is initiated, but that information can be mapped, transformed or supplemented as the transaction moves between institutions. Differences in implementation, local requirements and underlying systems can affect what ultimately reaches downstream participants.
This has practical consequences for both processing and risk management.
Consistency Matters to Financial Crime Controls
Cross-border payments can involve several institutions applying sanctions, AML and other financial crime controls to the same transaction.
Richer structured information can give those controls more context, particularly where identifying information about parties and the purpose of a transaction is available consistently. It can also make information easier to analyse automatically than equivalent information contained in unstructured fields.
But inconsistent or incomplete data can have the opposite effect. It may contribute to screening alerts, requests for additional information, manual investigations or payment delays.
The benefit therefore depends partly on whether different participants can interpret and use the information consistently, not simply exchange it.
Exceptions Reveal Where the Chain Is Not Working
Repair rates, message rejections and manual interventions can provide useful evidence of where cross-border processing is breaking down.
Repeated exceptions may indicate problems with data quality, message validation, mapping between systems or differences in how counterparties implement particular requirements. They can also show where the intended benefits of greater automation are being lost through manual intervention.
Traceability matters for the same reason. When a payment is delayed, rejected or investigated, firms need to understand what happened to the relevant information as it travelled through the chain and where an inconsistency was introduced.
For risk leaders, this makes cross-border ISO 20022 implementation more than an interoperability question. It is also about whether payment information retains sufficient integrity and meaning across organisational and jurisdictional boundaries to support effective processing and control.
New Data Creates New Governance Questions
As structured payment data becomes more important to processing and control decisions, firms need clarity over who is accountable for that information as it moves through the organisation.
The data-quality risk is one issue. The governance question is different: who is responsible for preventing, identifying and resolving those weaknesses?
Payment information may move between customer channels, payment platforms, financial crime systems, ledgers, processors, banks and other external providers. Different teams may own individual systems or processes without anyone having clear accountability for the integrity of the information across the complete flow.
Who Owns the Data as It Moves?
Operations may own the payment process. Technology may own the systems through which the data travels. Financial Crime may depend on particular fields for screening and monitoring. Data teams may establish standards and quality requirements. Third parties may transform information before it reaches another participant.
This creates the possibility of accountability gaps between systems and functions, particularly when a problem originates in one area but affects a control owned elsewhere.
Effective governance should therefore establish who is responsible for:
defining critical payment-data requirements;
validating information where appropriate;
monitoring data quality and exceptions;
approving material mappings and transformations;
investigating and remediating data-quality issues; and
assessing whether changes to data affect downstream controls.
The objective is not to create a separate governance structure for ISO 20022. Existing governance should instead reflect how payment information moves through the organisation and which decisions and controls depend upon it.
Governance Must Follow the Data
Clear ownership at source is not enough when information changes as it moves between systems.
Firms should be able to identify where material payment information originates, which systems or providers can transform it and which downstream processes rely upon it. Changes to mappings, validation rules or interfaces may therefore require consideration beyond the technology team implementing them.
Richer payment messages can also contain more detailed information about individuals and transactions. Retention, access and privacy requirements should consequently form part of the governance model, alongside data quality and control effectiveness.
The practical objective is clear accountability across the data lifecycle: who owns the information, who can change it, who depends on it and who acts when something goes wrong.
For firms migrating to ISO 20022, the governance challenge is therefore broader than technical message conversion. They need to understand whether data mappings, ownership and downstream controls remain effective as richer information moves between new and legacy systems.
Third-Party Risk in an ISO 20022 Payment Chain
Few firms control the complete journey of an ISO 20022 payment.
Processors, banks, payment infrastructures, technology vendors and other service providers may receive, validate, transform or transmit payment information before it reaches its destination. Their role therefore affects more than service availability: it can affect the integrity and usability of the data itself.
This is where the existing article's generic vendor-risk checklist can be replaced with a more payment-specific question:
What happens to our payment data when it passes through a third party?
A provider may:
preserve the information received;
enrich it with additional data;
map it into different internal structures;
transform it into another message format; or
truncate fields that its systems or downstream interfaces cannot accommodate.
Each can affect processes elsewhere in the payment chain.
A transformation that appears technically successful, for example, could remove information subsequently required for sanctions screening, reconciliation or investigation. A provider may support ISO 20022 externally while relying on legacy formats internally, creating points where information is converted and potentially lost.
Look Beyond ISO 20022 Compatibility
Asking whether a provider “supports ISO 20022” is therefore insufficient.
Firms need to understand how the provider handles the data, including which message elements it supports, where transformations occur, how exceptions are managed and whether information remains available when incidents or investigations require it.
Changes introduced by providers also matter. A modification to mapping logic or validation rules can alter payment processing or downstream control outcomes even when the firm's own systems have not changed.
This creates a dependency between third-party change management and the firm's own control environment.
Concentration can deepen that dependency. Where the same processor, bank or technology provider supports several products or payment routes, a data-handling problem can affect multiple services simultaneously rather than remaining confined to one transaction flow.
Third-party oversight should therefore extend beyond uptime, service levels and contractual compliance. For ISO 20022, firms also need visibility of where external providers sit in the payment-data chain, what they do to the information and which controls or services would be affected if that information were degraded, changed or unavailable.
Read more about Third Party Risk Management: Third-Party Risk Management Policy: Framework, Standards, and Examples →
What Should Risk Leaders Monitor?
The benefits of ISO 20022 should ultimately be visible in how payment processes and controls perform.
That means monitoring should go beyond whether implementation has been completed or messages are being exchanged successfully. Risk leaders need evidence of whether structured data is improving processing, reducing avoidable intervention and supporting more effective controls.

These indicators become more useful when considered together.
A falling straight-through-processing rate alongside increasing payment repairs, for example, may indicate deterioration in incoming data or message handling. Rising false positives following a change in structured fields could point to control calibration rather than increased underlying financial crime risk.
Reconciliation exceptions concentrated around a particular provider may reveal a mapping or transformation problem outside the firm's own systems.
Trends also matter more than isolated measurements. A low level of exceptions may be acceptable, but persistent deterioration can provide early evidence that data quality, interoperability or control effectiveness is changing.
Risk reporting should therefore help management understand not only how ISO 20022 processing is performing, but where the expected risk-management benefits are failing to materialise and why.
Questions Boards and Risk Leaders Should Ask
Boards do not need detailed oversight of individual ISO 20022 message fields. They do need to understand whether investment in richer payment data is translating into better controls, more reliable operations and improved risk visibility.
Six questions can help test that.
1. Are we receiving richer payment data, or actually using it?
Technical adoption does not demonstrate risk-management value. Management should be able to explain which additional information is being used by screening, monitoring, reconciliation, analytics and other material controls, and what has changed as a result.
2. Where can important information be lost or changed?
Boards and risk leaders should understand the material points where payment data is mapped, transformed, truncated or moved between systems, particularly where downstream controls depend on that information.
3. Have our controls changed as the data has changed?
If screening rules, monitoring models and operational controls continue to use the same information in the same way, richer messages may deliver limited additional value. Management should understand whether control design and calibration have evolved alongside the available data.
4. Can we demonstrate better outcomes?
Benefits should be evidenced rather than assumed. Depending on the business model, that might include fewer payment repairs, higher straight-through processing, improved reconciliation, better-quality financial crime alerts, fewer false positives or more effective investigations.
5. Which third parties can change or constrain the data we depend upon?
Management should know which providers receive, transform, enrich or truncate material payment information and whether those dependencies could affect processing or control effectiveness.
6. Are new data dependencies reflected in our risk framework?
As controls and decisions become more dependent on structured payment information, weaknesses in data quality, lineage and external processing can become material operational risks. Those dependencies should be visible within relevant risk assessments, controls, reporting and governance rather than treated solely as an ISO 20022 implementation issue.
Collectively, these questions move the discussion beyond “Have we implemented ISO 20022?” towards the more important question: “What has changed in the way we understand and manage payment risk?”
Building a governance framework for your FinTech?
Whether you are preparing for FCA authorisation, strengthening board oversight, implementing Consumer Duty, or scaling your governance arrangements as your business grows, Aevitium helps FinTechs design governance frameworks that are proportionate, practical, and aligned with regulatory expectations.

Conclusion: The Standard Creates the Opportunity, Not the Outcome
ISO 20022 represents an important change in the information infrastructure supporting payments. Richer, more structured and machine-readable data can provide greater transaction context, support automation and give financial institutions more information with which to identify and manage risk.
But the standard does not determine what firms do with that capability.
Better financial crime decisions depend on how enriched data is incorporated into screening, monitoring and investigations. More efficient processing depends on data quality and effective automation. Interoperability does not create operational resilience unless alternative arrangements have actually been built and tested. And richer information creates little risk-management value if it is lost, transformed incorrectly or unavailable to the controls that need it.
The opportunity is therefore broader than technical migration.
Firms need to understand which information matters, where it comes from, how it moves through the payment chain, which controls depend upon it and whether it is improving decisions and outcomes in practice.
As ISO 20022 becomes embedded across payment infrastructures, the differentiator will increasingly be less about whether organisations can exchange richer payment messages and more about how effectively they govern, analyse and act on the information those messages contain.
That is where the risk-management value of ISO 20022 ultimately sits.
FAQ: ISO 20022 and Risk Management
Does ISO 20022 automatically improve risk management?
No. ISO 20022 provides richer, more structured and machine-readable payment information, but the risk-management benefit depends on how firms use that information. Data quality, system mappings, control design, analytics and governance all influence whether additional payment data results in better risk identification and decision-making.
Does ISO 20022 reduce financial crime risk?
ISO 20022 does not prevent fraud, money laundering or sanctions breaches. Richer transaction and party information can provide additional context for screening, monitoring and investigations. Whether this improves financial crime outcomes depends on the quality of the underlying data and how effectively firms incorporate it into their controls and analytical models.
What happens if ISO 20022 data is incomplete or inaccurate?
Poor-quality structured data can affect automated processing, screening, reconciliation and risk analytics. It may contribute to false positives, payment repairs, exceptions or incorrect decisions. Because structured information can be processed automatically at scale, systematic data-quality weaknesses can also affect large transaction populations quickly.
Can firms lose ISO 20022 data as payments move between systems?
Yes. Payment information may be mapped, reformatted, transformed or truncated as it moves through internal systems, legacy technology and external providers. Firms should understand their material data flows and where information relied upon by downstream controls could be changed or lost.
Does ISO 20022 make payment systems operationally resilient?
Not by itself. A common messaging standard can support interoperability and reduce some integration barriers, but it does not provide alternative payment rails, redundant infrastructure, additional capacity or automatic failover. Operational resilience still depends on capabilities such as tested recovery arrangements, viable alternatives and effective incident management.
What should firms ask third-party providers about ISO 20022?
Firms should look beyond whether a provider simply states that it “supports ISO 20022.” Relevant questions include which message elements it supports, whether information is transformed or truncated, how mappings are controlled, how exceptions are handled, what changes occur within subcontracted services and how data integrity is maintained throughout processing.
How can firms tell whether ISO 20022 is delivering risk-management benefits?
Evidence will depend on the firm's business model, but useful measures can include payment repair and rejection rates, straight-through-processing rates, reconciliation exceptions, manual interventions, screening false positives and data-quality issues. Trends and relationships between these measures can be more informative than any single metric.
Who should be responsible for ISO 20022 data governance?
Responsibility is likely to span Payments, Operations, Technology, Data, Risk and Financial Crime rather than sit with a single function. Firms should nevertheless establish clear accountability for critical data requirements, mappings and transformations, data-quality monitoring, control dependencies and remediation when material information is inaccurate or lost.
Is ISO 20022 implementation finished once a firm can send and receive compliant messages?
Technical compatibility is only part of implementation. Firms should also consider whether their internal systems retain and use the richer information, whether relevant controls have been adapted, whether data transformations are understood and whether the additional information is producing measurable improvements in processing or risk management.
What should Boards know about ISO 20022?
Boards do not need detailed knowledge of individual message structures. Where ISO 20022 is material to the firm's payment activities, they should understand the significant operational and data dependencies, whether expected benefits are being realised, whether material risks are reflected in the risk framework and whether management can evidence improvements in controls and outcomes.